
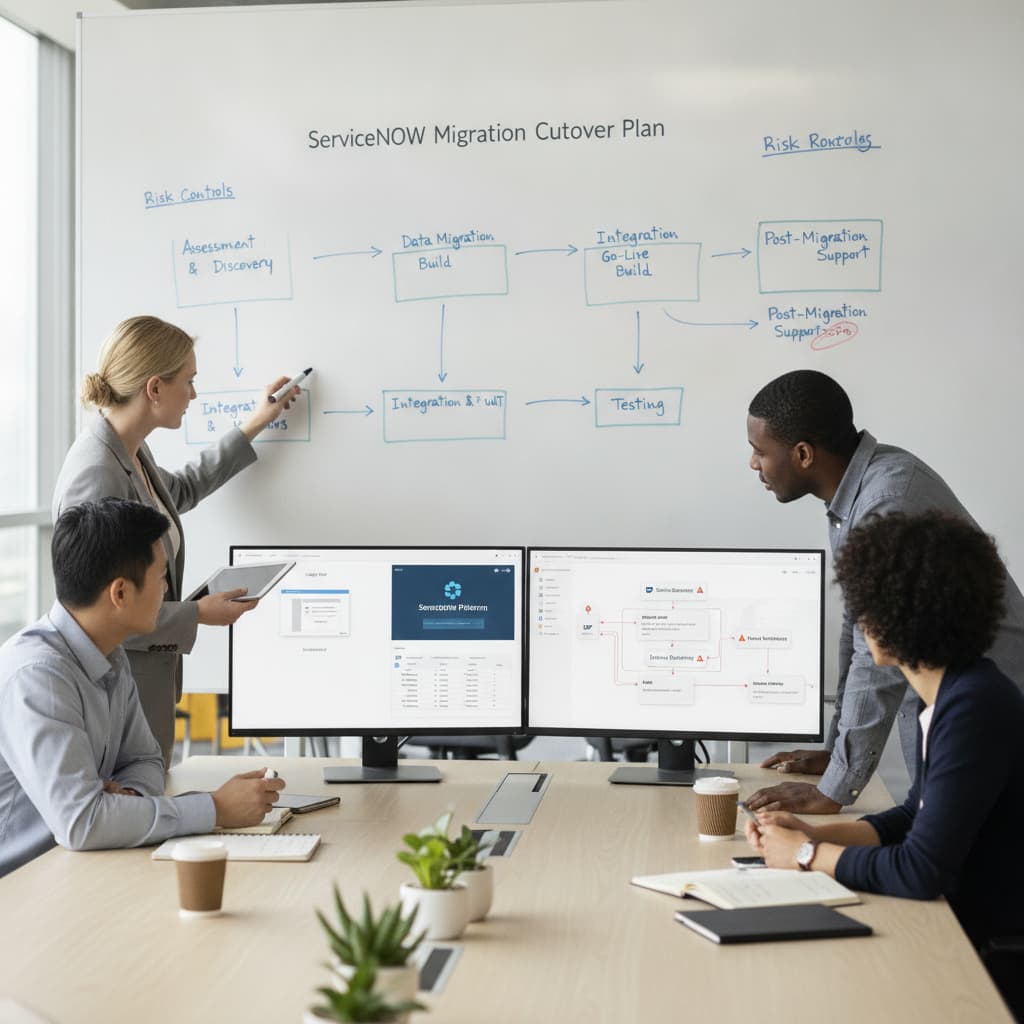
ServiceNow migration cutover plan: data, integrations and risk controls
A practical ServiceNow migration cutover plan helps reduce risk, protect service continuity, validate integrations and support confident ITSM modernisation.
Read more →NIS2 compliance is won or lost in day-to-day operations: an incident workflow that meets the 24-hour deadline, a CMDB that shows which assets are critical, and evidence an auditor accepts. SMC Consulting turns the directive's obligations into processes, configuration and dashboards inside the ITSM tool you already run, alongside your legal and security advisers.



The NIS2 Directive (EU) 2022/2555 covers 18 sectors, from energy, transport, banking and health to digital providers, manufacturing and public administration. Medium and large organisations in those sectors are in scope, as essential or important entities; some are in scope whatever their size.
This page explains how NIS2 obligations translate into IT service management. It is not legal advice; we work alongside your lawyers and security advisers. Last reviewed: 1 October 2026.
Most obligations land on processes your ITSM already runs: incidents, changes, assets, suppliers. We start from what you have. Our advice is independent. If you choose HaloITSM, we can also supply the licences as its certified partner, and we tell you so up front.
When the controls run in the tool, timestamps, approvals and reports are produced by daily work rather than assembled before an audit.
Your lawyers interpret the law and your security team runs the defences; we make the obligations work in operations.
Discovery with Lansweeper feeds the CMDB, so the list of critical assets stays current without manual updates.
Articles 20 and 21 of the directive set management accountability and the risk-management measures; article 23 sets the reporting obligations. Each one has a home in IT service management, and a piece of evidence that proves it works.
Changes to critical services are assessed for security risk, approved and traceable.
Significant incidents are recognised, escalated and reported on time, with a clear owner.
Critical assets and the services they support are known, owned and up to date.
Suppliers of critical services are identified, assessed and linked to the services they affect.
Continuity and recovery plans exist for critical services and are tested.
Management bodies approve the measures and oversee their implementation, as article 20 of the directive requires.
Four steps from a first diagnostic to an audit-ready file. For the data model behind it, read our NIS2 CMDB requirements guide and ITAM and NIS2 incident response.
Joint assessment of your scope (essential / important) and of your current ITSM maturity. Initial mapping of critical assets, and identification of the gaps between where you are and what NIS2 requires. Deliverable: NIS2 diagnostic report + ITSM baseline.
Detailed gap analysis, prioritisation by urgency and impact, estimated effort (man-days) and costs (licences, configuration, training). A plan you can defend to your board and your CFO. Deliverable: Gap analysis + costed 3-year NIS2 roadmap.
Configuration of your ITSM tool (existing or new) against the four obligations: a CMDB enriched with regulatory criticality, a 24h/72h/30-day incident workflow, a documented catalogue of measures, and governance dashboards. Documentation produced as we go. Deliverable: A NIS2 setup, live and documented inside your ITSM.
Audit simulation, full-scale test of the incident notification procedure, completeness check of the compliance file, and training for the executive committee on its personal obligations. Deliverable: Audit-ready compliance file + trained teams.
As soon as a significant incident is detected, an early warning goes to the CSIRT or authority. In the ITSM, a major-incident trigger starts the timer and drafts the notification from a template.
An update with a first assessment of severity, impact and indicators of compromise. The incident record already holds the timeline, affected services and actions taken.
A detailed description, root cause, mitigation and cross-border impact. Problem management produces the root-cause analysis; the report is generated from the records.
Tells you what the directive and the national law require, and whether you are in scope. Essential, but it does not configure your incident workflow.
Tests and strengthens your defences: SOC, pentests, hardening. Also essential, but rarely touches your service management processes.
Makes the obligations run every day in your tools: the 24-hour trigger, the critical-asset view, the evidence. That is our part, alongside the other two.
In Belgium, the CCB's CyberFundamentals framework (CyFun) is one of the reference frameworks for demonstrating NIS2 compliance, alongside ISO/IEC 27001. It comes in four levels (Small, Basic, Important and Essential), and the level you aim for depends on your risk profile and your NIS2 category.
Many CyFun controls are evidenced by your ITSM tool: asset inventory and ownership, change control, incident detection and response, supplier management, and the review of measures by management. Configuring those processes properly gives your assessor evidence that already exists, instead of documents written for the audit.
More on the asset side: IT asset management and the HaloITSM CMDB.
A practical checklist to see where your ITSM stands against NIS2, process by process. Leave your details and a consultant goes through it with you.
If you operate in one of the 18 critical sectors and employ more than 50 people (or turn over more than €10M), NIS2 most likely applies. If you are unsure, the 30-minute consultation is enough to settle your exact scope.
The CCB in Belgium and ANSSI in France publish official scope guidance: ccb.belgium.be, cyber.gouv.fr.
Article 23 of the directive sets three steps for significant incidents: an early warning within 24 hours of becoming aware of the incident, an incident notification within 72 hours with a first assessment, and a final report within one month. National laws set the exact channel, such as the CCB in Belgium.
It runs the processes the directive relies on (incident, change, asset, supplier and continuity management) and records what happens in them. Configured well, it starts the reporting clock, shows which assets are critical and produces the evidence an auditor asks for.
CyFun is the CCB's cybersecurity framework, with four assurance levels. In Belgium it is one of the reference frameworks, alongside ISO/IEC 27001, for showing that your NIS2 measures are in place. Many of its controls are evidenced in your ITSM tool.
Essential entities: up to €10M or 2% of worldwide turnover, whichever is higher. Important entities: up to €7M or 1.4% of worldwide turnover, whichever is higher. For essential entities, NIS2 also allows managers to be temporarily suspended from executive duties.
Yes. Incident, change and asset processes already exist; NIS2 asks you to make them reliable, timely and provable. We start by auditing what your tool does today before proposing anything new.
Between 3 and 12 months, depending on your starting maturity, your scope and the state of your current ITSM tool. The week-one diagnostic gives a precise estimate of effort and cost.
See where your incident, asset and change processes stand against NIS2, then book a free 30-minute audit to set priorities.
A practical ServiceNow migration cutover plan helps reduce risk, protect service continuity, validate integrations and support confident ITSM modernisation.
Read more →
SMC Consulting joins the Lansweeper partner ecosystem to connect asset discovery with HaloITSM, ServiceNow and Freshservice for a complete, current CMDB.
Read more →
Discover how Green ITAM helps measure your IT asset carbon footprint, improve CSRD IT readiness, connect asset data, and support credible sustainability reporting.
Read more →